Security Management Systems
Shows that you manage security risks across your operations and supply chain.
A complete documentation kit written to ISO 28000:2022 with Amendment 1:2024: manual, policies, procedures, SOPs, forms, registers, process maps, indicator and risk frameworks, audit and management review packs, an implementation roadmap, sector guides and commercial templates, with every clause mapped to the document that meets it, and control of critical assets, security risk, access, cargo and seals, personnel, business partners, the information interface, plans and drills built into the system.
- Edition 2022
- 147 Word + 32 Excel files
- One organization
- Downloads open 7 days after payment
You need this if
- You move, store or handle goods in the supply chain.
- Clients or customs programmes ask about cargo, seals and access control.
- You need security risk assessment, vetting and drills on record.
What you get, in numbers
Counted from the files in the pack. Every file title is listed further down.
What this toolkit is not
Worth knowing before you buy.
Not the certificate
Certification is decided by an independent certification body after it audits a system you have run for some months, with records. No toolkit can guarantee it.
Not the ISO text
The standard is copyrighted and sold by ISO and national standards bodies. Buy your own copy. The toolkit describes requirements in its own words.
Not a consultant
We do not assess your organization. You review, adapt and approve every document before you use it.
What’s inside
15 numbered folders. Open any folder to see the title of every file in it. Titles only: the files themselves are delivered after payment.
00Start Here
Six guides: read-me, how to implement with an initial review checklist, documentation structure, quick start, an ISO 28000:2022 clause mapping guide, and a certification preparation guide.
6 files
- WordSH-001 Read Me Guide
- WordSH-002 How to Implement Guide
- WordSH-003 Documentation Structure Guide
- WordSH-004 Quick Start Guide
- WordSH-005 ISO 28000-2022 Clause Mapping Guide
- WordSH-006 Certification Preparation Guide
01Master Index
One Excel register of every controlled document: number, title, type, owner, department, retention and clause, with review dates and overdue flags.
1 file
- ExcelREG-01 Master Document Register
02Manual
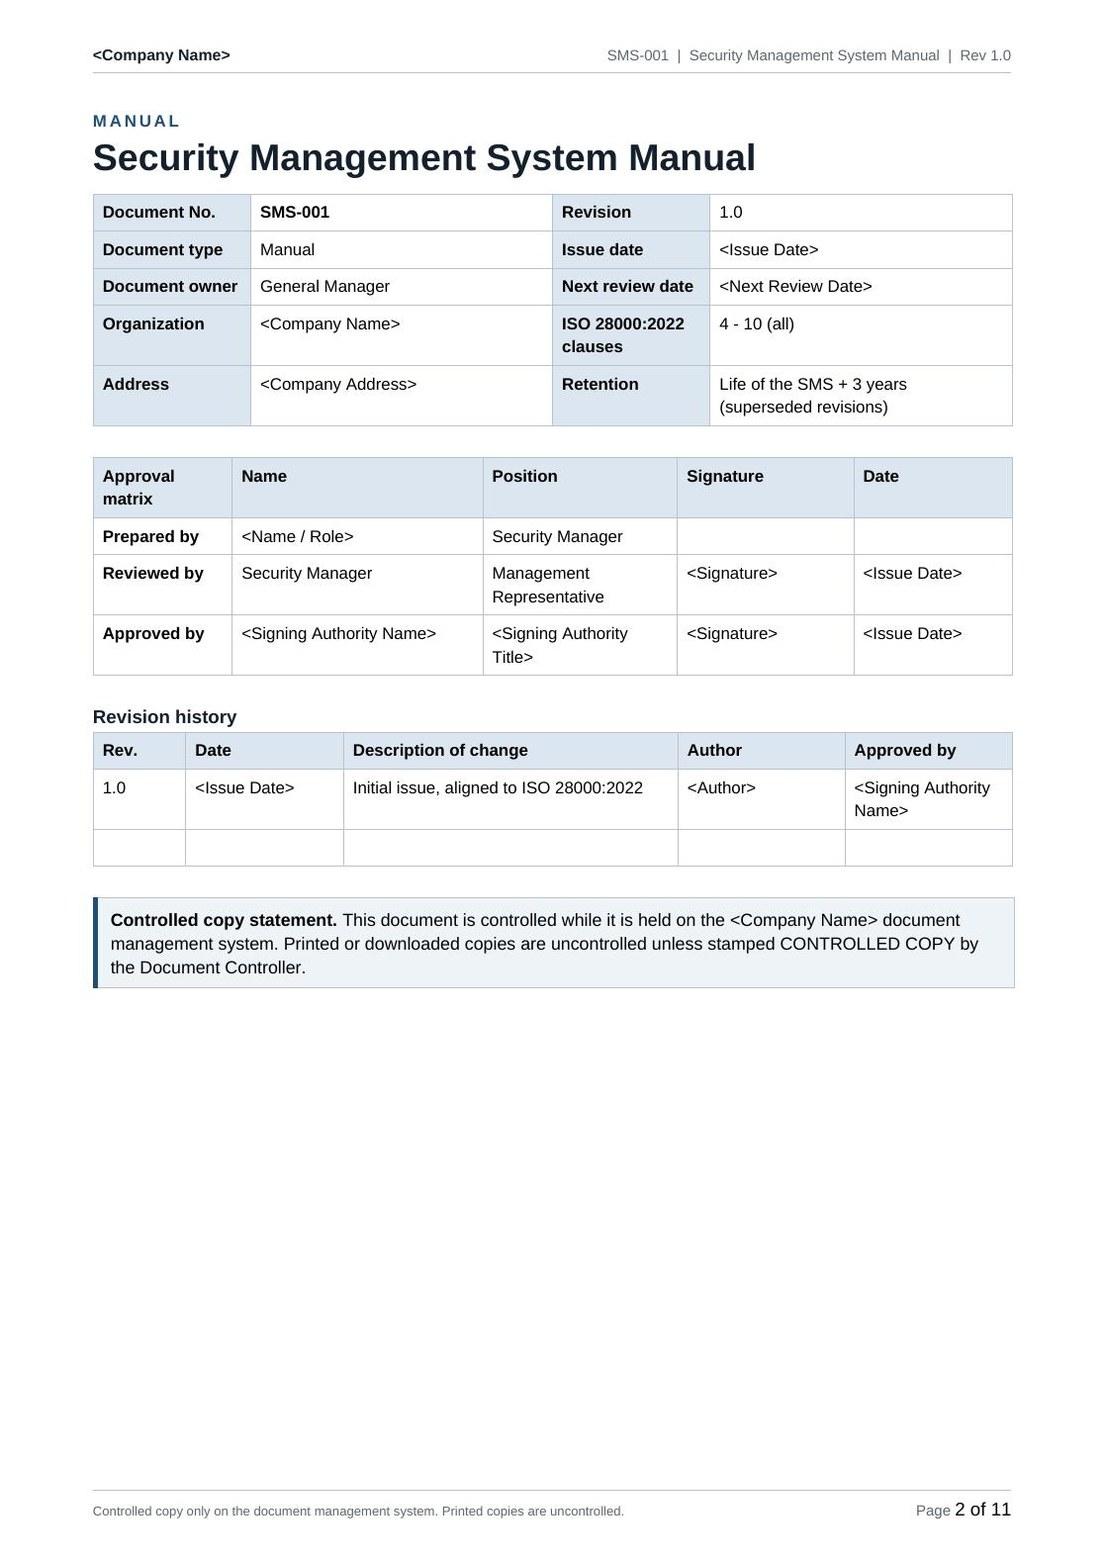
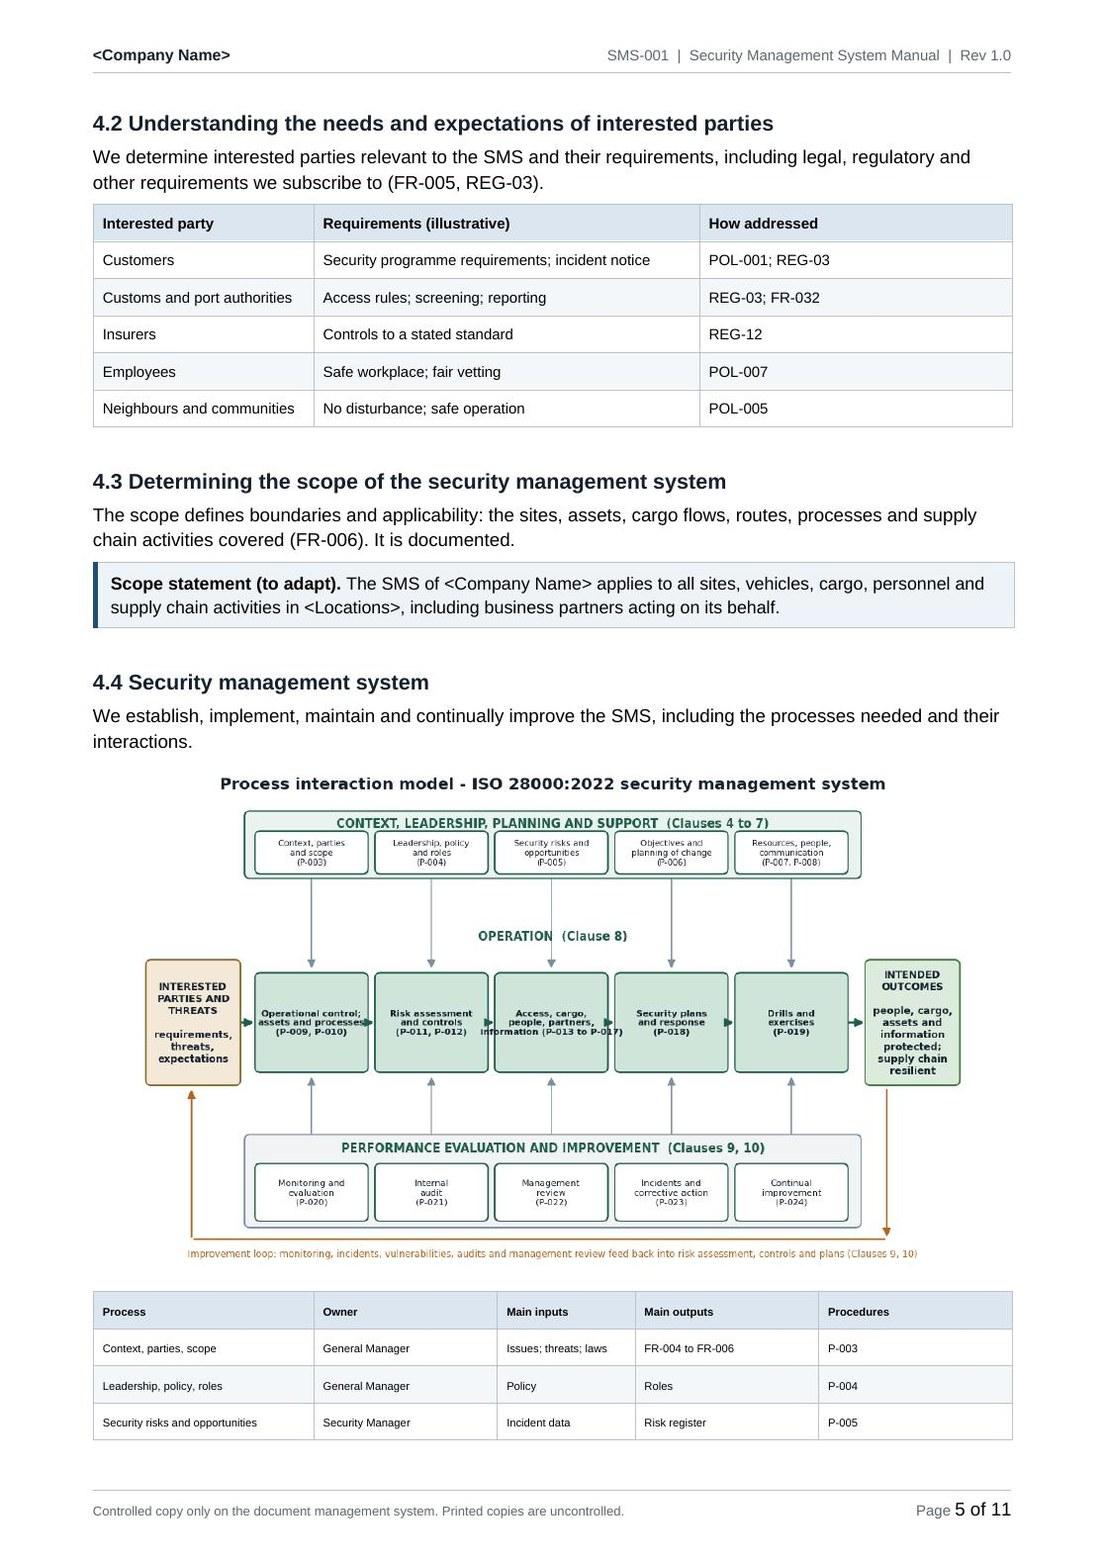
The Security Management System Manual, section-numbered to match clauses 4 to 10: context including the climate decision, requirements, leadership with the authority to stop an operation, planning, support, operation including critical asset identification, risk assessment, controls, access and physical security, cargo and seals, personnel, partners, the information interface and security plans, performance evaluation and improvement.
1 file
- WordSMS-001 Security Management System Manual
03Procedures (P-001 to P-024)
Document and record control, context and scope, leadership and roles, security risks and opportunities, objectives and planned change, resources and competence, awareness and communication, operational control, process and asset identification, risk assessment and treatment, controls and verification, access control and physical security, cargo seals and chain of custody, personnel vetting, business partners, the information interface, security plans and incident response, drills, monitoring, internal audit, management review, corrective action and improvement. Each has a flowchart, responsibility table, controls, risk and indicator matrices.
24 files
- WordP-001 Document Control Procedure
- WordP-002 Record Control Procedure
- WordP-003 Context, Interested Parties and Scope Procedure
- WordP-004 Leadership, Policy and Roles Procedure
- WordP-005 Security Risks and Opportunities Procedure
- WordP-006 Security Objectives and Planning of Changes Procedure
- WordP-007 Resources and Competence Procedure
- WordP-008 Awareness and Communication Procedure
- WordP-009 Operational Planning and Control Procedure
- WordP-010 Process, Activity and Asset Identification Procedure
- WordP-011 Security Risk Assessment and Treatment Procedure
- WordP-012 Security Controls Procedure
- WordP-013 Access Control and Physical Security Procedure
- WordP-014 Cargo, Seals and Chain of Custody Procedure
- WordP-015 Personnel Security and Vetting Procedure
- WordP-016 Business Partner and Supply Chain Security Procedure
- WordP-017 Information Security Interface Procedure
- WordP-018 Security Plans and Incident Response Procedure
- WordP-019 Security Drills and Exercises Procedure
- WordP-020 Monitoring, Measurement and Evaluation Procedure
- WordP-021 Internal Audit Procedure
- WordP-022 Management Review Procedure
- WordP-023 Nonconformity, Incident and Corrective Action Procedure
- WordP-024 Continual Improvement Procedure
04Policies (POL-001 to POL-012)
Security policy, document control, records and confidentiality, security risk management, access control and physical security, cargo and conveyance security, personnel security, business partner security, information security interface, security plans and incident response, competence and communication, and audit, review and improvement.
12 files
- WordPOL-001 Security Policy
- WordPOL-002 Document Control Policy
- WordPOL-003 Records and Confidentiality Policy
- WordPOL-004 Security Risk Management Policy
- WordPOL-005 Access Control and Physical Security Policy
- WordPOL-006 Cargo and Conveyance Security Policy
- WordPOL-007 Personnel Security Policy
- WordPOL-008 Business Partner Security Policy
- WordPOL-009 Information Security Interface Policy
- WordPOL-010 Security Plans and Incident Response Policy
- WordPOL-011 Competence, Awareness and Communication Policy
- WordPOL-012 Audit, Review and Improvement Policy
05SOP Library (SOP-001 to SOP-022)
Step-by-step task instructions with flowcharts and acceptance criteria: risk workshops, critical asset identification, site assessment, access and visitor control, patrols and CCTV, seal application and verification, conveyance inspection and handover, vetting, induction, partner assessment, interface checks, incident response and investigation, drills, reporting, audit, corrective action and near-miss handling.
22 files
- WordSOP-001 Document Issue and Withdrawal
- WordSOP-002 Records Filing and Archiving
- WordSOP-003 Context Review Workshop
- WordSOP-004 Security Risk Workshop
- WordSOP-005 Critical Process and Asset Identification
- WordSOP-006 Site Security Assessment
- WordSOP-007 Access Control Operation
- WordSOP-008 Visitor and Contractor Management
- WordSOP-009 Patrols and CCTV Monitoring
- WordSOP-010 Seal Application and Verification
- WordSOP-011 Conveyance Inspection and Cargo Handover
- WordSOP-012 Personnel Vetting
- WordSOP-013 Security Induction and Briefing
- WordSOP-014 Business Partner Security Assessment
- WordSOP-015 Information Security Interface Check
- WordSOP-016 Security Incident Response
- WordSOP-017 Security Incident Investigation
- WordSOP-018 Security Drill
- WordSOP-019 Security Performance Reporting
- WordSOP-020 Internal Audit Conduct
- WordSOP-021 Corrective Action Tracking
- WordSOP-022 Vulnerability and Near-Miss Handling
06Forms (FR-001 to FR-051)
Fifty-one forms. Each comes with field descriptions, a blank form that prints on its own, and a completed example record.
51 files
- WordFR-001 Document Change Request
- WordFR-002 Document Review Record
- WordFR-003 Record Disposal Authorization
- WordFR-004 Context and Climate Review
- WordFR-005 Interested Party and Requirements Review
- WordFR-006 SMS Scope Statement
- WordFR-007 Roles, Responsibilities and Authorities Record
- WordFR-008 Policy Communication Record
- WordFR-009 Security Risk and Opportunity Assessment
- WordFR-010 Security Objectives Plan
- WordFR-011 SMS Change Record
- WordFR-012 Resource Request
- WordFR-013 Competence Assessment
- WordFR-014 Training Record
- WordFR-015 Communication Plan
- WordFR-016 Operational Control Plan
- WordFR-017 Critical Process and Asset Identification
- WordFR-018 Security Risk Assessment
- WordFR-019 Security Risk Treatment Plan
- WordFR-020 Control Design and Test Record
- WordFR-021 Site Security Assessment
- WordFR-022 Access Authorization and Visitor Record
- WordFR-023 Security Patrol and Inspection Record
- WordFR-024 Seal and Conveyance Inspection Record
- WordFR-025 Cargo Handover Record
- WordFR-026 Personnel Vetting Record
- WordFR-027 Security Induction and Briefing Record
- WordFR-028 Business Partner Security Assessment
- WordFR-029 Business Partner Security Review
- WordFR-030 Information Security Interface Check
- WordFR-031 Security Plan
- WordFR-032 Security Incident Report
- WordFR-033 Security Incident Investigation Report
- WordFR-034 Drill Plan
- WordFR-035 Drill Record
- WordFR-036 Security Indicator Definition Sheet
- WordFR-037 Security Performance Report
- WordFR-038 Annual Audit Programme
- WordFR-039 Audit Plan
- WordFR-040 Internal Audit Checklist
- WordFR-041 Audit Report
- WordFR-042 Auditor Competence Record
- WordFR-043 Management Review Agenda
- WordFR-044 Management Review Minutes
- WordFR-045 Management Review Action Plan
- WordFR-046 NCR Form
- WordFR-047 Corrective Action Request
- WordFR-048 Corrective Action Effectiveness Review
- WordFR-049 Vulnerability and Near-Miss Report
- WordFR-050 Improvement Suggestion Form
- WordFR-051 Improvement Project Charter
07Registers (REG-01 to REG-18)
Eighteen Excel registers with examples, drop-down lists, automatic calculations, due dates and flags: critical assets, site assessments (grades and next date), access authorizations (vetting level against zone, passes returned), seals and cargo (discrepancy and time to report), personnel vetting (expired vetting), business partners, controls (verification and failures), incidents (time to report, evidence held, investigation time), vulnerabilities and near misses, drills, indicators, corrective actions and audits.
18 files
- ExcelREG-01 Document Register
- ExcelREG-02 Record Register
- ExcelREG-03 Security Requirements Register
- ExcelREG-04 Security Risk and Opportunity Register
- ExcelREG-05 Critical Process and Asset Register
- ExcelREG-06 Security Objectives and Plans Register
- ExcelREG-07 Site Security Assessment Register
- ExcelREG-08 Access Authorization Register
- ExcelREG-09 Seal and Cargo Integrity Register
- ExcelREG-10 Personnel Vetting and Training Register
- ExcelREG-11 Business Partner Register
- ExcelREG-12 Security Controls Register
- ExcelREG-13 Security Incident Register
- ExcelREG-14 Vulnerability and Near-Miss Register
- ExcelREG-15 Drill Register
- ExcelREG-16 Security Indicators Register
- ExcelREG-17 Nonconformity and Corrective Action Register
- ExcelREG-18 Audit Register
08Process Maps
Eight swimlane maps with inputs, outputs, owners and indicator links: context and risk, leadership and resources, controls, access and physical security, cargo and seals, personnel and partners, incidents and drills, and monitoring and improvement.
8 files
- WordPM-01 Context, Requirements, Critical Assets and Security Risk Process Map
- WordPM-02 Leadership, Objectives, Resources and Communication Process Map
- WordPM-03 Operational Control and Security Controls Process Map
- WordPM-04 Access Control and Physical Security Process Map
- WordPM-05 Cargo, Seals and Chain of Custody Process Map
- WordPM-06 Personnel and Business Partner Security Process Map
- WordPM-07 Information Interface, Security Plans, Incidents and Drills Process Map
- WordPM-08 Monitoring, Audit, Review and Improvement Process Map
09Indicators & Risk
85 indicators with formulas and targets in a filterable matrix, corporate and department frameworks, a balanced scorecard, a 5 x 5 risk matrix with 37 example risks, and an improvement opportunity matrix with 25 examples.
6 files
- WordKPI-01 Corporate Indicator Framework
- WordKPI-02 Department Indicator Framework
- ExcelKPI-03 Balanced Scorecard
- ExcelKPI-04 Process Indicator Matrix
- ExcelRSK-01 Risk Management Matrix
- ExcelRSK-02 Opportunity Matrix
10Audit
Annual audit programme covering every clause, site and critical route, audit plan with physical tests, notification, auditor competence matrix, a 33-question checklist by clause, a complete audit report and a findings tracker.
7 files
- WordAUD-01 Annual Audit Programme
- WordAUD-02 Audit Plan
- WordAUD-03 Audit Notification
- ExcelAUD-04 Auditor Competence Matrix
- ExcelAUD-05 Audit Checklist by Clause
- WordAUD-06 Audit Report
- ExcelAUD-07 Follow-up Tracker
11Management Review
Agenda, inputs checklist covering every input of clause 9.3 including incidents, vulnerabilities and drills, completed sample minutes with the required outputs, action plan and a dashboard.
5 files
- WordMRV-01 Management Review Agenda
- WordMRV-02 Management Review Inputs Checklist
- WordMRV-03 Management Review Minutes Template
- ExcelMRV-04 Management Review Action Plan
- ExcelMRV-05 Management Review Dashboard
12Implementation
An eight-month roadmap with activities, milestones, deliverables and responsibilities, and a task tracker.
2 files
- WordIMP-01 Implementation Roadmap
- ExcelIMP-02 Implementation Tracker
13Customization
Guides with risks, controls and indicators for logistics and port services, container terminals, road transport, warehousing, airports and air cargo, manufacturers and exporters, retail and e-commerce, pharmaceuticals and high-value goods, energy and critical utilities, and government and customs.
10 files
- WordCUS-01 Logistics, Freight Forwarding and Port Services Customization Guide
- WordCUS-02 Container Terminals and Ports Customization Guide
- WordCUS-03 Road Transport and Trucking Fleets Customization Guide
- WordCUS-04 Warehousing, Distribution and Fulfilment Customization Guide
- WordCUS-05 Airports and Air Cargo Customization Guide
- WordCUS-06 Manufacturers and Exporters Customization Guide
- WordCUS-07 Retail and E-commerce Supply Chains Customization Guide
- WordCUS-08 Pharmaceutical and High-Value Goods Customization Guide
- WordCUS-09 Oil, Gas, Energy and Critical Utilities Customization Guide
- WordCUS-10 Government, Customs and Public Critical Infrastructure Customization Guide
14Commercial
Gap assessment checklist, certification readiness checklist, implementation and training proposal templates, consultancy agreement template and audit preparation checklist.
6 files
- ExcelCOM-01 Gap Assessment Checklist
- ExcelCOM-02 Certification Readiness Checklist
- WordCOM-03 Implementation Proposal Template
- WordCOM-04 Training Proposal Template
- WordCOM-05 Consultancy Agreement
- ExcelCOM-06 Audit Preparation Checklist
Sample pages
Pages from the delivered files, before your company details are applied.
After you download
The order most organizations follow.
Before you buy
Is the text of ISO 28000 included?
No. The standard is copyrighted by ISO and sold by ISO and national standards bodies; Amendment 1:2024 (climate action changes) is free from ISO. Buy your own copy of ISO 28000:2022. The toolkit describes requirements in its own words and maps every clause to the document that meets it, so you can check each against the standard.
Which edition does the kit follow?
ISO 28000:2022 (second edition, March 2022) with Amendment 1:2024, which is the current edition. It replaced ISO 28000:2007, which had a different structure, and follows the common management system structure. The transition period for certificates to the 2007 edition has ended; confirm with your certification body.
Does the kit make us secure or replace security law and advice?
No. A security management system reduces risk but cannot prevent every incident. The kit does not replace national security law, customs, aviation or maritime security rules, customer security programmes or specialist security advice.
Are the examples and figures real data?
No. Names, sites, zones, seal and vetting rules, risk ratings, thresholds, timescales and cases in example records are fictional and marked as examples. Set your own from your risk assessment and the rules that apply to you.
Can we edit the documents after purchase?
Yes. Files are delivered as standard, unlocked .docx and .xlsx files. Nothing is watermarked or restricted. Items such as prepared-by names and company profile facts are left for you to complete.
Will this get us certified on its own?
The toolkit gives you a complete, clause-mapped documentation baseline and tools for operating the system. Certification is decided by independent bodies after they audit a working system, including site visits, sampling of records, checks of controls and interviews, so you must run the system for some months first. Neither a toolkit nor a management system guarantees certification or the prevention of incidents.
How long can we download the files?
For 7 days from payment. In that time you can enter your company details, correct them and regenerate, and download as often as you need. After 7 days the purchase stays in your account history, but the download closes. Save the ZIP somewhere safe.
What if we need the files again later?
Buying the same toolkit again is a new order with its own 7-day download window. Each purchase is listed separately in your account.
Licence
One purchase licenses one organization to use, edit and adapt the documents for its own management system. You may not resell, share or publish the toolkit or its templates. Each file carries a footer line with the buyer’s email and order number. Full wording is in the Terms & licence.