Information Security Management
Shows that you assess information security risks and run the controls that treat them.
A complete documentation kit written to ISO/IEC 27001:2022 including Amendment 1:2024 (climate action changes): manual, policies, procedures, SOPs, forms, registers, process maps, indicator and risk frameworks, audit and management review packs, an implementation roadmap, sector guides and commercial templates, with every clause mapped to the document that meets it, and risk assessment, risk treatment and a Statement of Applicability for all 93 Annex A controls built into the system.
- Edition 2022
- 178 Word + 31 Excel files
- One organization
- Downloads open 7 days after payment
You need this if
- You hold client data, run software or hosting, or provide managed IT services.
- Security questionnaires and vendor reviews are slowing down your sales.
- You need a Statement of Applicability for the 93 Annex A controls.
Look here instead if the question you are being asked is about personal data and privacy, not security in general. ISO/IEC 27701:2025 Privacy Information Management Systems →
What you get, in numbers
Counted from the files in the pack. Every file title is listed further down.
What this toolkit is not
Worth knowing before you buy.
Not the certificate
Certification is decided by an independent certification body after it audits a system you have run for some months, with records. No toolkit can guarantee it.
Not the ISO text
The standard is copyrighted and sold by ISO and national standards bodies. Buy your own copy. The toolkit describes requirements in its own words.
Not a consultant
We do not assess your organization. You review, adapt and approve every document before you use it.
What’s inside
15 numbered folders. Open any folder to see the title of every file in it. Titles only: the files themselves are delivered after payment.
00Start Here
Six guides: read-me, how to implement with an initial review checklist, documentation structure, quick start, an ISO/IEC 27001:2022 clause and Annex A mapping guide covering Amendment 1:2024, and a certification preparation guide.
6 files
- WordSH-001 Read Me Guide
- WordSH-002 How to Implement Guide
- WordSH-003 Documentation Structure Guide
- WordSH-004 Quick Start Guide
- WordSH-005 ISO-IEC 27001-2022 Clause Mapping Guide
- WordSH-006 Certification Preparation Guide
01Master Index
One Excel register of every controlled document: number, title, type, owner, department, retention and clause, with review dates and overdue flags.
1 file
- ExcelREG-01 Master Document Register
02Manual
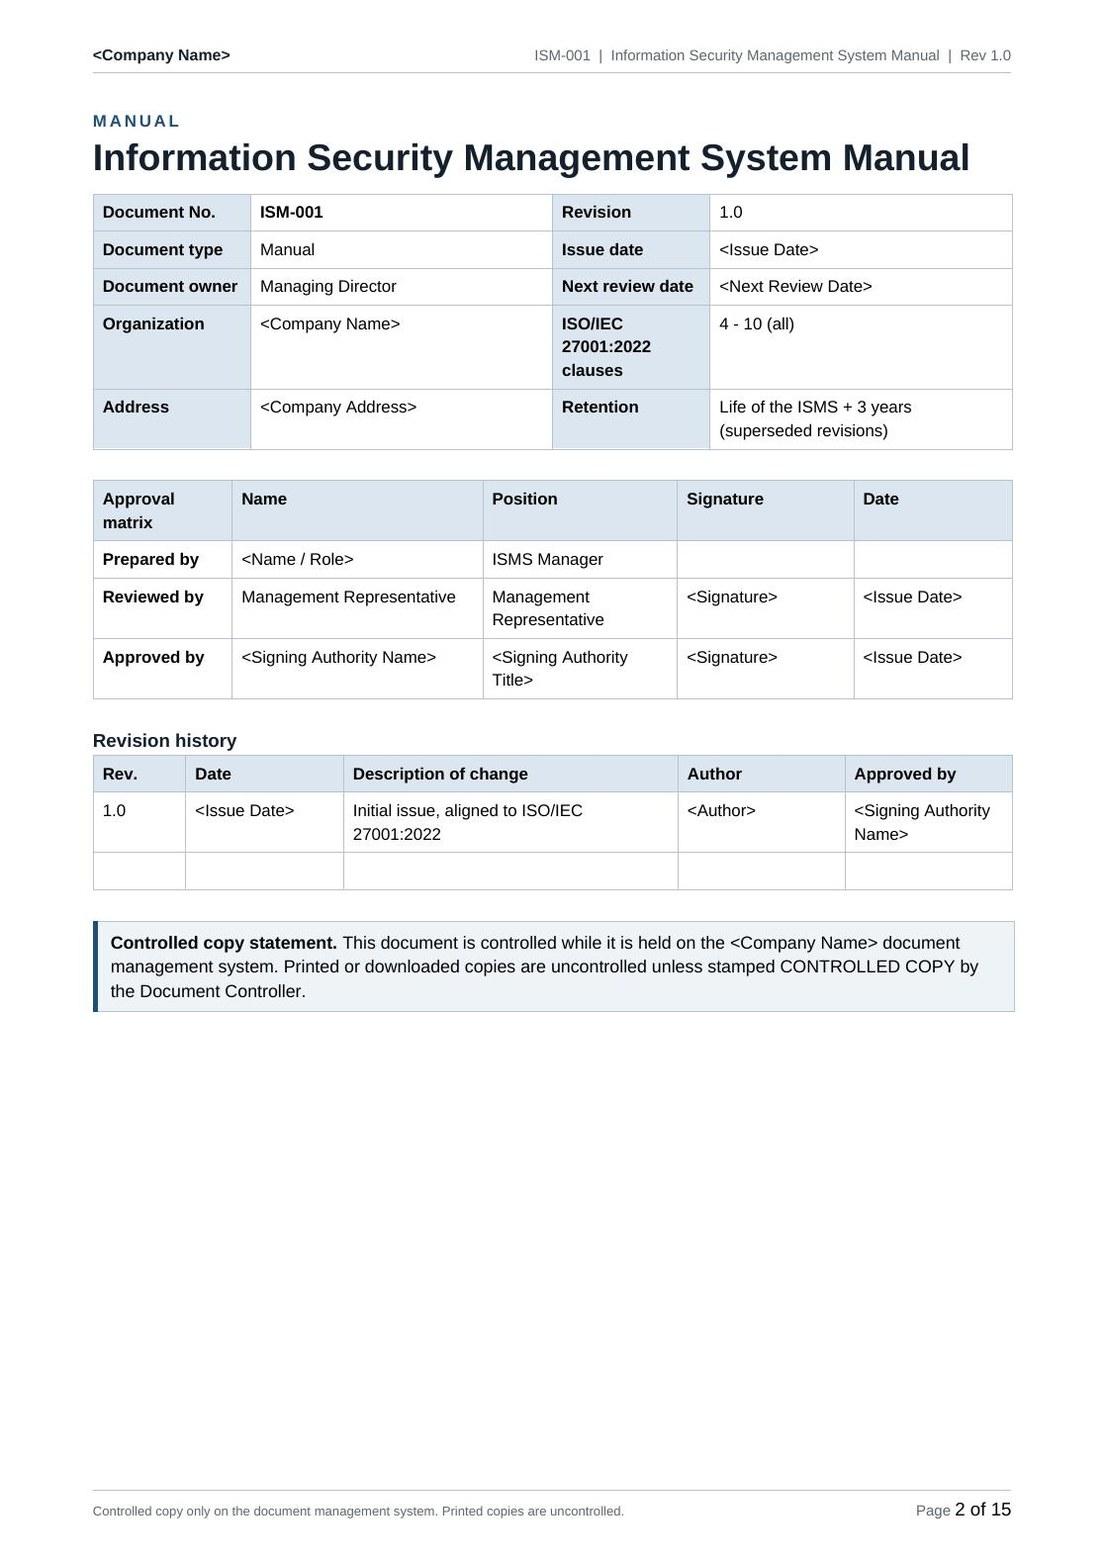
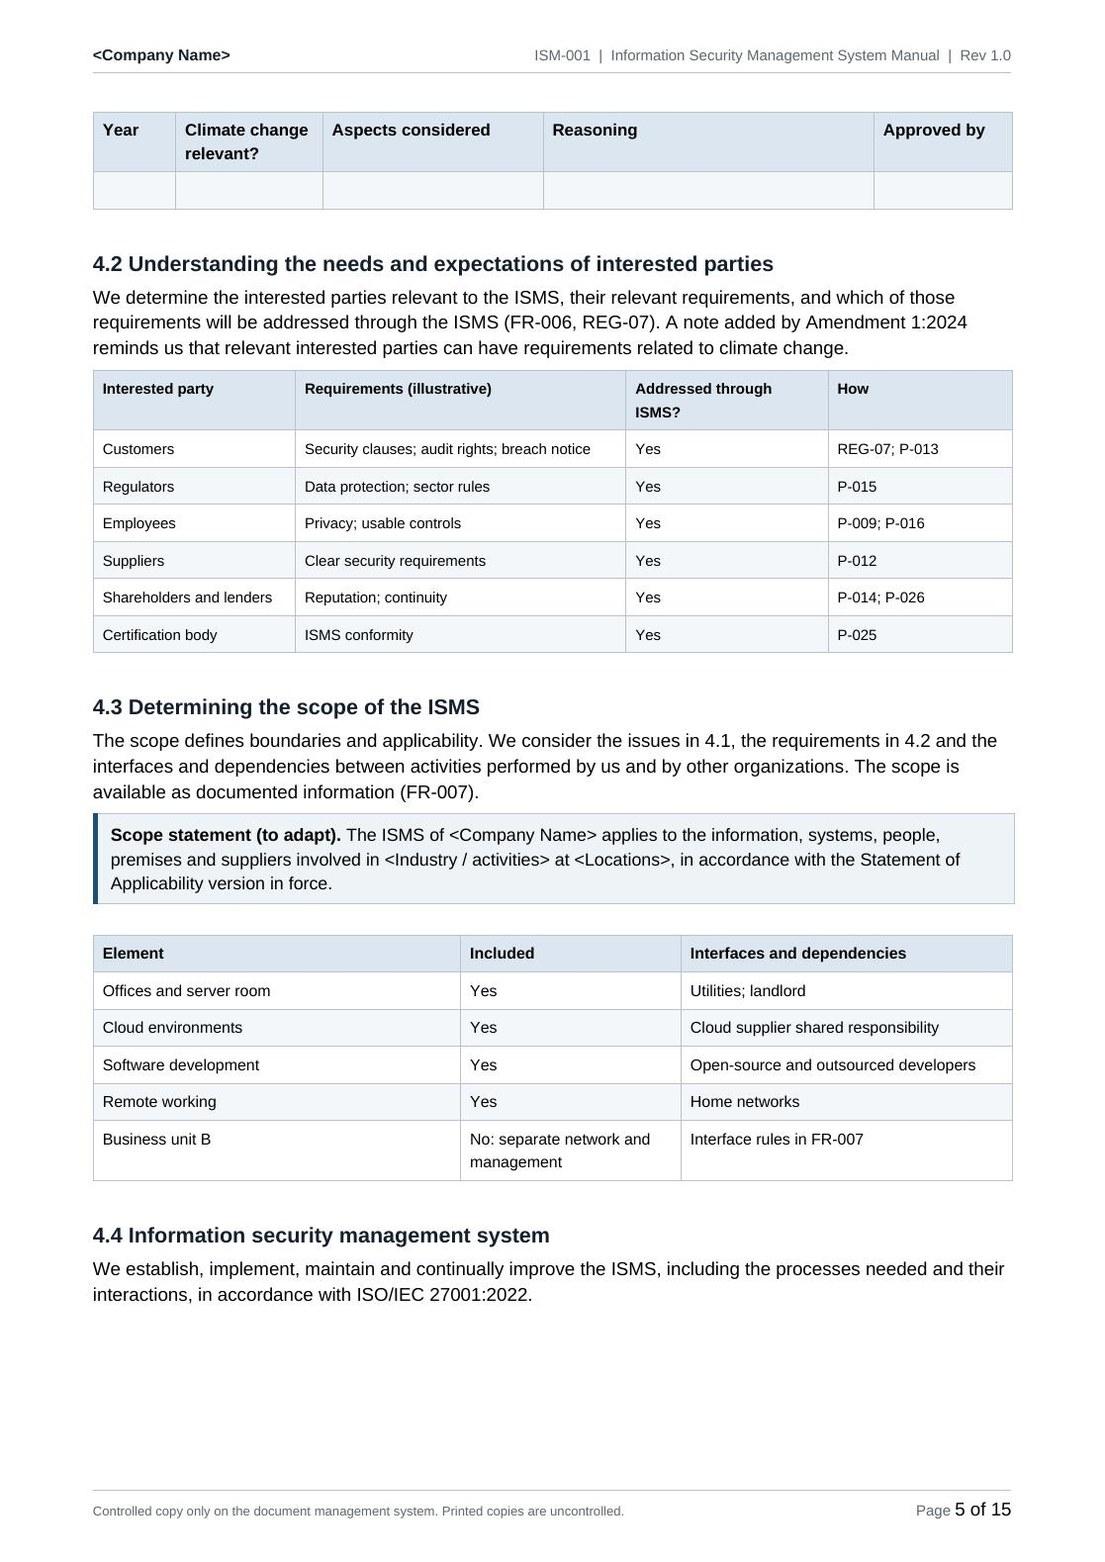
The Information Security Management System Manual, section-numbered to match clauses 4 to 10: context and the climate decision, leadership, risk assessment and treatment, the Statement of Applicability, objectives, planning of changes, support, operation, performance evaluation, audit, management review and improvement, with a map of all 93 Annex A controls.
1 file
- WordISM-001 Information Security Management System Manual
03Procedures (P-001 to P-028)
Document and record control, context and scope, leadership, risk assessment, risk treatment and the Statement of Applicability, objectives and changes, competence, awareness, assets and classification, access and identity, suppliers and cloud, incidents, continuity, legal and privacy, personnel, physical security, configuration and change, vulnerabilities, logging and monitoring, network and endpoint, cryptography, secure development, measurement, internal audit, management review, corrective action and improvement. Each has a flowchart, responsibility table, controls, risk and indicator matrices.
28 files
- WordP-001 Document Control Procedure
- WordP-002 Record Control Procedure
- WordP-003 Context, Interested Parties and Scope Procedure
- WordP-004 Leadership, Roles and Responsibilities Procedure
- WordP-005 Information Security Risk Assessment Procedure
- WordP-006 Risk Treatment and Statement of Applicability Procedure
- WordP-007 Objectives and Planning of Changes Procedure
- WordP-008 Resources and Competence Procedure
- WordP-009 Awareness, Training and Communication Procedure
- WordP-010 Asset Management and Classification Procedure
- WordP-011 Access Control and Identity Management Procedure
- WordP-012 Supplier and Cloud Service Security Procedure
- WordP-013 Incident Management Procedure
- WordP-014 Business Continuity and ICT Readiness Procedure
- WordP-015 Legal, Regulatory and Privacy Compliance Procedure
- WordP-016 Personnel Security Procedure
- WordP-017 Physical and Environmental Security Procedure
- WordP-018 Configuration and Change Management Procedure
- WordP-019 Vulnerability and Malware Management Procedure
- WordP-020 Logging, Monitoring and Threat Intelligence Procedure
- WordP-021 Network and Endpoint Security Procedure
- WordP-022 Cryptography and Data Protection Procedure
- WordP-023 Secure Development Procedure
- WordP-024 Monitoring, Measurement and Evaluation Procedure
- WordP-025 Internal Audit Procedure
- WordP-026 Management Review Procedure
- WordP-027 Nonconformity and Corrective Action Procedure
- WordP-028 Continual Improvement Procedure
04Policies (POL-001 to POL-014)
Information security policy, document control, record retention, risk management, legal and contractual requirements, competence and awareness, access control, asset management and acceptable use, supplier security, incident management, business continuity, cryptography, secure development and change, and physical, remote working and device rules.
14 files
- WordPOL-001 Information Security Policy
- WordPOL-002 Document Control Policy
- WordPOL-003 Record Retention Policy
- WordPOL-004 Risk Management Policy
- WordPOL-005 Legal, Regulatory and Contractual Requirements Policy
- WordPOL-006 Competence, Awareness and Personnel Security Policy
- WordPOL-007 Access Control Policy
- WordPOL-008 Asset Management and Acceptable Use Policy
- WordPOL-009 Supplier Security Policy
- WordPOL-010 Incident Management Policy
- WordPOL-011 Business Continuity and ICT Readiness Policy
- WordPOL-012 Cryptography and Data Protection Policy
- WordPOL-013 Secure Development and Change Policy
- WordPOL-014 Physical, Remote Working and Device Policy
05SOP Library (SOP-001 to SOP-030)
Step-by-step task instructions with flowcharts and acceptance criteria: risk workshops, Statement of Applicability, awareness and phishing simulation, asset inventory, access provisioning and review, privileged access, supplier and cloud review, incident response, evidence handling, backup and restore tests, continuity exercises, joiners and leavers, physical access, disposal, hardening, patching, log review, endpoints, keys, code review and internal audit.
30 files
- WordSOP-001 Document Issue and Withdrawal
- WordSOP-002 Records Filing and Archiving
- WordSOP-003 Context Review Workshop
- WordSOP-004 Security Steering Committee Meeting
- WordSOP-005 Risk Assessment Workshop
- WordSOP-006 Risk Treatment and SoA Maintenance
- WordSOP-007 Change Assessment
- WordSOP-008 Security Induction and Awareness Briefing
- WordSOP-009 Phishing Simulation and Awareness Campaign
- WordSOP-010 Asset Inventory Maintenance
- WordSOP-011 Information Classification and Labelling
- WordSOP-012 User Access Provisioning and Removal
- WordSOP-013 Periodic Access Review
- WordSOP-014 Privileged Access Management
- WordSOP-015 Supplier Onboarding Security Review
- WordSOP-016 Cloud Service Security Review
- WordSOP-017 Security Incident Response
- WordSOP-018 Evidence Collection and Handling
- WordSOP-019 Backup and Restore Test
- WordSOP-020 Business Continuity Exercise
- WordSOP-021 Employee Onboarding and Offboarding Security
- WordSOP-022 Visitor and Physical Access Control
- WordSOP-023 Secure Disposal of Equipment and Media
- WordSOP-024 Configuration Baselines and Hardening
- WordSOP-025 Patch and Vulnerability Management
- WordSOP-026 Log Review and Alert Handling
- WordSOP-027 Endpoint and Mobile Device Management
- WordSOP-028 Cryptographic Key Management
- WordSOP-029 Secure Code Review and Release
- WordSOP-030 Internal Audit Planning and Conduct
06Forms (FR-001 to FR-068)
Sixty-eight forms. Each comes with field descriptions, a blank form that prints on its own, and a completed example record.
68 files
- WordFR-001 Document Change Request
- WordFR-002 Document Distribution Log
- WordFR-003 Document Review Record
- WordFR-004 Record Disposal Authorization
- WordFR-005 Context and Climate Review
- WordFR-006 Interested Party Requirements Review
- WordFR-007 ISMS Scope Statement
- WordFR-008 Security Steering Committee Minutes
- WordFR-009 Roles and Responsibilities Record
- WordFR-010 Risk Assessment Record
- WordFR-011 Risk Criteria Sheet
- WordFR-012 Risk Treatment Plan
- WordFR-013 Statement of Applicability Review Record
- WordFR-014 Objective and Plan Form
- WordFR-015 Change Request and Security Assessment
- WordFR-016 Post-Change Review
- WordFR-017 Role Competence Definition
- WordFR-018 Competence Assessment Form
- WordFR-019 Resource Request
- WordFR-020 Awareness Training Attendance Record
- WordFR-021 Training Evaluation Form
- WordFR-022 Communication Plan Record
- WordFR-023 Information Classification Record
- WordFR-024 Asset Return Checklist
- WordFR-025 Access Request and Approval
- WordFR-026 Access Review Record
- WordFR-027 Privileged Access Record
- WordFR-028 Supplier Security Assessment
- WordFR-029 Supplier Agreement Security Checklist
- WordFR-030 Supplier Review Record
- WordFR-031 Cloud Service Assessment
- WordFR-032 Security Event Report
- WordFR-033 Incident Record
- WordFR-034 Post-Incident Review
- WordFR-035 Business Impact Analysis
- WordFR-036 Continuity Test Report
- WordFR-037 Backup Restore Test Record
- WordFR-038 Legal Requirement Identification
- WordFR-039 Privacy Impact Assessment
- WordFR-040 Onboarding Security Checklist
- WordFR-041 Offboarding Security Checklist
- WordFR-042 Visitor Log
- WordFR-043 Physical Security Inspection
- WordFR-044 Configuration Baseline Record
- WordFR-045 Vulnerability Scan Review
- WordFR-046 Patch Record
- WordFR-047 Log Review Record
- WordFR-048 Threat Intelligence Brief
- WordFR-049 Endpoint Compliance Check
- WordFR-050 Network Security Review
- WordFR-051 Key Management Record
- WordFR-052 Secure Development Checklist
- WordFR-053 Security Test Report
- WordFR-054 Security Metrics Report
- WordFR-055 Indicator Definition Sheet
- WordFR-056 Annual Audit Programme
- WordFR-057 Audit Plan
- WordFR-058 Internal Audit Checklist
- WordFR-059 Audit Report
- WordFR-060 Auditor Competence Record
- WordFR-061 Management Review Agenda
- WordFR-062 Management Review Minutes
- WordFR-063 Management Review Action Plan
- WordFR-064 NCR Form
- WordFR-065 Corrective Action Request
- WordFR-066 Corrective Action Effectiveness Review
- WordFR-067 Improvement Suggestion Form
- WordFR-068 Improvement Project Charter
07Registers (REG-01 to REG-17)
Seventeen Excel registers with examples, drop-down lists, automatic calculations, due dates and overdue flags, including a Statement of Applicability listing all 93 Annex A controls with applicability, justification, status and a completeness check: documents, records, assets, risks, treatment plans, legal and contractual requirements, objectives, competence, suppliers and cloud services, privileged access, incidents, vulnerabilities, continuity, nonconformities, audits and changes.
17 files
- ExcelREG-01 Document Register
- ExcelREG-02 Record Register
- ExcelREG-03 Information Asset Register
- ExcelREG-04 Risk Register
- ExcelREG-05 Risk Treatment Plan Register
- ExcelREG-06 Statement of Applicability
- ExcelREG-07 Legal, Regulatory and Contractual Requirements Register
- ExcelREG-08 Objectives and Programme Register
- ExcelREG-09 Training and Competence Register
- ExcelREG-10 Supplier and Cloud Service Register
- ExcelREG-11 Privileged and Third-Party Access Register
- ExcelREG-12 Incident Register
- ExcelREG-13 Vulnerability and Patch Register
- ExcelREG-14 Business Continuity and BIA Register
- ExcelREG-15 Nonconformity and Corrective Action Register
- ExcelREG-16 Audit Register
- ExcelREG-17 Change Register
08Process Maps
Eight swimlane maps with inputs, outputs, owners and indicator links: context and leadership, risk assessment and treatment, assets and access, suppliers and compliance, incidents and continuity, people, technical operations, and audit and review.
8 files
- WordPM-01 Context, Leadership and Objectives Process Map
- WordPM-02 Risk Assessment and Treatment Process Map
- WordPM-03 Assets, Access and Identity Process Map
- WordPM-04 Suppliers, Cloud and Legal Compliance Process Map
- WordPM-05 Incident and Continuity Process Map
- WordPM-06 People, Awareness and Personnel Security Process Map
- WordPM-07 Technical Security Operations Process Map
- WordPM-08 Evaluation, Audit, Review and Improvement Process Map
09Indicators & Risk
85 information security indicators with formulas and targets in a filterable matrix, corporate and department frameworks, a balanced scorecard, a 5 x 5 risk matrix with 38 example risks, and an opportunity matrix with 25 examples.
6 files
- WordKPI-01 Corporate Security Indicator Framework
- WordKPI-02 Department Indicator Framework
- ExcelKPI-03 Balanced Scorecard
- ExcelKPI-04 Process Indicator Matrix
- ExcelRSK-01 Risk Management Matrix
- ExcelRSK-02 Opportunity Matrix
10Audit
Annual audit programme covering every clause and Annex A control, audit plan, notification, auditor competence matrix, a 60-question checklist by clause and control theme, a complete audit report and a findings tracker.
7 files
- WordAUD-01 Annual Audit Programme
- WordAUD-02 Audit Plan
- WordAUD-03 Audit Notification
- ExcelAUD-04 Auditor Competence Matrix
- ExcelAUD-05 Audit Checklist by Clause
- WordAUD-06 Audit Report
- ExcelAUD-07 Follow-up Tracker
11Management Review
Agenda, inputs checklist, completed sample minutes with the required results, action plan and a dashboard.
5 files
- WordMRV-01 Management Review Agenda
- WordMRV-02 Management Review Inputs Checklist
- WordMRV-03 Management Review Minutes Template
- ExcelMRV-04 Management Review Action Plan
- ExcelMRV-05 Management Review Dashboard
12Implementation
An eight-month roadmap with activities, milestones, deliverables and responsibilities, and a task tracker.
2 files
- WordIMP-01 Implementation Roadmap
- ExcelIMP-02 Implementation Tracker
13Customization
Guides with information assets, risks and indicators for software and SaaS, IT and managed services, financial services, healthcare, e-commerce, telecommunications, manufacturing with operational technology, professional services, public sector, and education.
10 files
- WordCUS-01 Software and SaaS Customization Guide
- WordCUS-02 IT Services and Managed Services Customization Guide
- WordCUS-03 Financial Services and Fintech Customization Guide
- WordCUS-04 Healthcare and Life Sciences Customization Guide
- WordCUS-05 E-commerce and Retail Customization Guide
- WordCUS-06 Telecommunications Customization Guide
- WordCUS-07 Manufacturing (IT and OT) Customization Guide
- WordCUS-08 Professional Services and Consultancy Customization Guide
- WordCUS-09 Government and Public Sector Customization Guide
- WordCUS-10 Education and Research Customization Guide
14Commercial
Gap assessment checklist, certification readiness checklist, implementation and training proposal templates, consultancy agreement template and audit preparation checklist.
6 files
- ExcelCOM-01 Gap Assessment Checklist
- ExcelCOM-02 Certification Readiness Checklist
- WordCOM-03 Implementation Proposal Template
- WordCOM-04 Training Proposal Template
- WordCOM-05 Consultancy Agreement
- ExcelCOM-06 Audit Preparation Checklist
Sample pages
Pages from the delivered files, before your company details are applied.
After you download
The order most organizations follow.
Before you buy
Is the text of ISO/IEC 27001:2022 included?
No. The standard is copyrighted by ISO and sold by ISO and national standards bodies. Buy your own copies of ISO/IEC 27001:2022 and 27002:2022, and download Amendment 1:2024 from ISO, which is free. The toolkit describes requirements in its own words and maps every clause to the document that meets it, so you can check each against the standard.
Which edition does the kit follow?
ISO/IEC 27001:2022 with Amendment 1:2024, which added the climate change decision to clause 4.1 and a note on climate requirements to clause 4.2. No newer edition has been published; the kit will need review when one is. Ask your certification body for its transition rules.
We are certified to ISO/IEC 27001:2013 or run an informal security programme. Does the kit help?
Yes. A clause mapping guide shows what the 2022 edition asks, including the new clause 6.3 and the restructured Annex A with 93 controls in four themes, and a gap assessment checklist helps you decide where to start.
Are the examples real data?
No. Names, certificates, limits and figures in example records are fictional and marked as examples. Replace them with your own. Risks, targets, legal duties and retention periods in particular depend on your business and where you operate.
Can we edit the documents after purchase?
Yes. Files are delivered as standard, unlocked .docx and .xlsx files. Nothing is watermarked or restricted. Items such as prepared-by names and company profile facts are left for you to complete.
Will this get us certified on its own?
The toolkit gives you a complete, clause-mapped documentation baseline and tools for operating the system. Certification is decided by an independent certification body after it audits a working system, including sampling of controls and interviews, so you must run the system for some months first. Neither a toolkit nor a management system guarantees freedom from incidents, legal compliance or certification.
How long can we download the files?
For 7 days from payment. In that time you can enter your company details, correct them and regenerate, and download as often as you need. After 7 days the purchase stays in your account history, but the download closes. Save the ZIP somewhere safe.
What if we need the files again later?
Buying the same toolkit again is a new order with its own 7-day download window. Each purchase is listed separately in your account.
Licence
One purchase licenses one organization to use, edit and adapt the documents for its own management system. You may not resell, share or publish the toolkit or its templates. Each file carries a footer line with the buyer’s email and order number. Full wording is in the Terms & licence.